Ship-Safe
Check your AI-built app for leaked keys, open databases and missing logins before launch.
The scanner is free. Both are delivered through Gumroad.
Why it matters
You built an app with Cursor, Claude Code, Lovable, Bolt, Replit or v0. It works. Before real users arrive, take 90 minutes to make sure it is not quietly leaking your API keys, your users' data or your Stripe account.
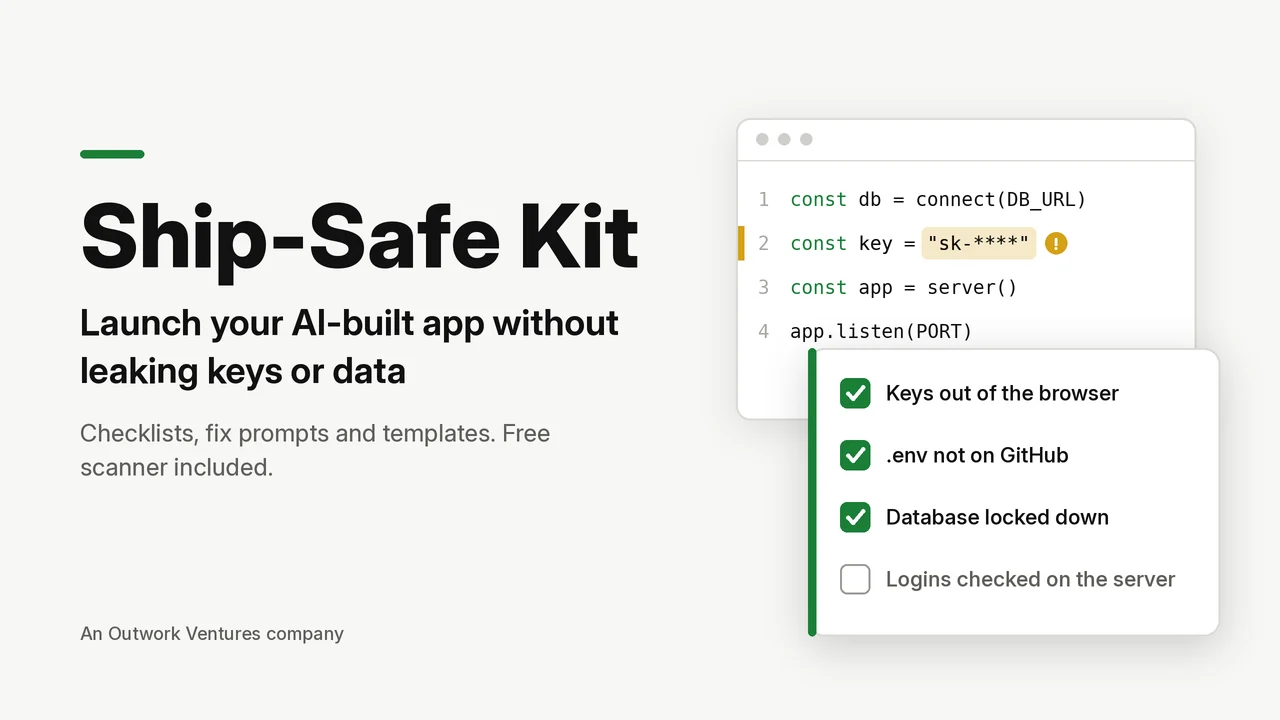
AI coding tools are fast, but they often leave the same few mistakes behind: secret keys in browser code, a .env file pushed to GitHub, Supabase tables with Row-Level Security switched off, pages that hide a button instead of checking who is logged in. Bots look for these around the clock.
Start free, then go further
Ship-Safe Scanner
A free offline tool that checks your project folder for exposed API keys, committed .env files and open databases before you launch. It checks for:
- Secret keys typed into code (OpenAI, Anthropic, Stripe, AWS, GitHub, Google and more)
- .env files in your project, and a .gitignore that does not cover them
- Supabase service_role keys or Stripe secret keys in browser code
- Open databases: Supabase tables without Row-Level Security, and Firebase rules that let anyone read or write
Each finding comes with a plain-English explanation and a copy-paste prompt to fix it. Keys are never shown in full in the report. It runs on your own computer with Python 3, needs nothing else installed and never uploads your code. Step-by-step instructions for Mac and Windows are included, plus a practice project so you can see what a finding looks like.
US$0
Get the free scannerShip-Safe Kit
A plain-English checklist that walks you through each common mistake. Every item tells you what to check, why it matters, and gives you an exact prompt to paste into your AI coding tool to fix it. No security background needed.
- Covers what a file scan cannot see: dashboard settings, logins, Stripe, CORS, rate limits and launch day itself
- Most people get through it in 60 to 90 minutes
- The free scanner is included
- Full refund within 14 days through your Gumroad receipt if it is not useful to you
US$39
Get the full kit, US$39What is inside the kit
- The Pre-Ship Checklist: secrets and .env files, .gitignore, Supabase and Row-Level Security, logins and admin checks, Stripe secret keys and webhooks, CORS, rate limits, dependencies
- A Launch-Day Runbook: what to do the day before, launch morning and the first 24 hours
- The Fix Prompts Library: copy-paste prompts for each problem, written for AI coding tools
- The Secrets Rotation Guide: what to do, in order, if a key has already leaked
- The Supabase RLS Checklist: lock down every table, with a logged-out and wrong-user test
- Drop-in templates: .env.example, .gitignore, Cursor rules and an AGENTS.md safety file for Claude Code and other agents
- The whole kit as one printable PDF, plus Markdown files you can keep in your project
Who it is for
Non-technical and semi-technical founders, makers and freelancers about to launch an app built with AI help.
It is not a replacement for a professional security audit if you handle sensitive regulated data such as health or financial records.
Questions
Is this a professional security audit?
No. It is a checklist and education tool that helps you catch the most common, most damaging mistakes. It cannot guarantee your app is secure.
I'm not technical. Can I use it?
Yes. It is written for you. Every term is explained, and every fix comes with a prompt you paste into your AI coding tool.
Which tools and stacks does it cover?
Cursor, Claude Code, Lovable, Bolt, Replit, v0, Windsurf and similar tools, and apps that use Supabase, Firebase, Stripe, Next.js or Vite.
How long does it take?
Most people get through it in 60 to 90 minutes.
What format is it?
A zip file with a printable PDF, Markdown checklists and template files.
What's the difference between the kit and the free scanner?
The scanner reads the files in your project folder and flags obvious problems. The kit also covers what a file scan cannot see: dashboard settings, logins, Stripe, CORS, rate limits and launch day itself.
Do I get updates?
Yes. Updated versions are added to the product, and you can download them again from your Gumroad library.
What if it's not for me?
Ask for a refund through your Gumroad receipt within 14 days.
Please note: Ship-Safe is a checklist and education tool. It is not a professional security audit and cannot guarantee that your app is secure.
Check it before you ship it. Start with the free scanner.
Ship-Safe is an Outwork Ventures company.